Enterprises should modernise data, access controls and oversight before letting software act across systems, advises various consultancies and this industry insider…
AI agents are moving enterprise AI beyond systems that answer questions towards software that can retrieve information, make recommendations and take action across business applications. But Arnold Consengco, Regional Vice President (North and South Asia), OutSystems, argues that the technology itself is not the main constraint.
“The harder question is whether the business underneath it is ready,” he said. His central warning is that organisations risk adding a new layer of complexity to old problems if they deploy agents on top of fragmented data, disconnected systems and poorly designed processes.
“An AI agent is still limited by what it can access,” he said. “If the information is incomplete, outdated or scattered across disconnected systems, the agent inherits those weaknesses.”
Start with the broken workflow
Consengco’s recommended starting point is not “where can we deploy an agent?” but “where is work breaking down today?”
That may be a manual review that takes days, an employee moving between several systems to complete one task, or a process delayed because information sits in different places. “These are often better starting points for AI than deploying an agent simply because the technology is available,” he said.
Once the problem is clear, organisations should work backwards. Consengco said leaders need to establish what information the agent needs, which systems it must connect to, where human judgment remains necessary, and what must change for the process to work better. This keeps modernisation targeted. Rather than replacing every legacy system, organisations can improve the data, interfaces and controls around the specific workflows where AI has a credible business return. Deloitte makes a comparable argument: the limiting factor is often not the model, but the enterprise environment in which it must operate.
Agents cannot repair weak foundations
Consengco is blunt about the limits of agentic AI. “New agents cannot overcome old foundations,” he said, arguing that enterprise cannot expect agents to “work around years of legacy technology, disconnected systems and fragmented data.”
The claim needs qualification: agents can sometimes bridge legacy gaps through APIs, retrieval layers, robotic process automation or human-in-the-loop review. However, they cannot safely compensate for poor data quality, undefined ownership, weak access controls or processes that were never designed to work together.
Consengco’s broader point remains sound: when AI moves from producing an answer to taking an action, weak foundations become operationally consequential. Data quality should therefore be treated as a gating condition, not a later optimisation.
Similarly, Taiwan’s Industrial Technology Research Institute argues that data and knowledge-base quality help determine how much autonomy an AI system can safely be given.
Classify autonomy before scaling
Not every agent warrants the same governance. Gartner recommends proportional controls based on an agent’s autonomy and scope, warning that uniform governance across all agents can itself lead to failure.
A practical classification is:
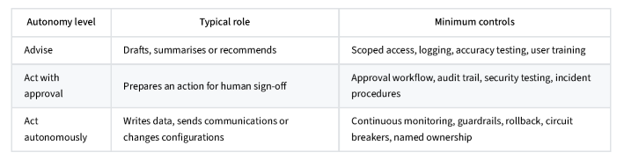
Consengco supports this direction. Organisations, he said, need to know “what their agents can access, what they are allowed to do and where a person still needs to make the final call.”
Gartner cautions that approval workflows can weaken under time pressure or approval fatigue, creating a false sense of safety while the attack surface expands. High-impact or irreversible actions should require explicit approval, clear ownership and the ability to halt or roll back the agent.
Treat agents as managed identities
An agent that can query systems, invoke tools or initiate transactions is not just another application. It is an operational actor that needs an identity, an owner and defined boundaries. Gartner recommends a central registry of agents, treating internal and third-party agents as distinct non-human identities, and applying dynamic least-privilege access controls. Rather than issuing static credentials, agents should receive temporary access that is revoked when a task is complete.
Similarly, Forrester’s AEGIS framework links identity and access management, AI governance and runtime security: organisations need to establish an agent’s identity and delegation relationships, define its purpose and accountability, and monitor or interrupt its actions in operation.
Build controls into operations
Consengco warns that without controls, enterprises may recreate the fragmented technology estates they are trying to fix: “different agents built by different teams, working across different systems with limited visibility over how they interact.”
Policy documents alone will not prevent that. Controls need to be embedded in the environment in which agents run. At a minimum, enterprises should implement:
- Data boundaries that define what an agent may retrieve, use or transmit
- Tool restrictions that limit which applications and actions are available
- Runtime monitoring of inputs, tool calls, actions and outcomes
- Separation between an agent’s proposal and the execution of high-risk actions
- Budget and usage limits to prevent runaway costs
- Incident procedures to isolate an agent, preserve evidence, revoke authority and recover unfinished work
Forrester advises organizations to test whether they can revoke an agent’s authority, halt execution, preserve evidence and locate unfinished work before relying on it in production.
Measure outcomes, not agent counts
Consengco argues that the number of agents deployed is not a useful measure of success. “Faster processes, lower costs, better decisions and stronger customer experiences are,” he said.
A more useful scorecard includes cycle time, error and rework rates, cost per transaction, decision quality, customer experience, security incidents and the proportion of workflows with clear human accountability.
Deloitte’s separate research found that 21% of organisations polled that were planning to deploy agentic AI had reported a mature governance model for autonomous agents.
Keep the architecture flexible
Consengco also advises against building an AI strategy around a single model or provider. “The market is changing too quickly to know which technology will be best suited for every use case a few years from now,” he said.
The more durable requirement is interoperability: the ability to connect agents to existing applications and data, replace components as needs change, and retain control over critical workflows and data.
That flexibility should not become an excuse for ungoverned experimentation. Every new agent, connector or third-party service should enter the same inventory, access-control and monitoring regime.
Overview: A pragmatic sequence
In short, fix the workflow, not just the technology:
- Select one high-friction workflow with measurable baseline metrics
- Map its data sources, systems, exceptions and approval points
- Classify the proposed agent’s autonomy level and risk
- Define its identity, permissions, data boundaries and audit requirements
- Pilot with human oversight and rollback controls
- Measure outcomes against the baseline before expanding
- Add agents only when governance, observability and ownership can scale with them
Consengco’s conclusion is a useful one, provided enterprises treat it as a discipline rather than a vendor pitch: “The companies that get the most from agentic AI will be those that use it as a reason to fix how work gets done, rather than as a way to avoid doing so.”